Practical Guide to Unifor Raiding Risk and Compliance
This guide examines Unifor Raiding from a compliance and risk-management perspective, helping organizations understand what tends to drive these events, how suppliers and workplaces prepare, and which controls reduce disruption. Objectively, the term is commonly used in workplace and sector reporting to describe targeted interventions. The article contextualizes expectations, stakeholder impacts, and practical governance steps.
Unifor Raiding: Key Compliance Priorities First
When organizations hear the phrase Unifor Raiding, the very important question is usually not “what is the word used for,” but how should we manage the operational, legal, and reputational risks that may follow. From an industry-expert standpoint, the highest-impact preparation involves clear governance, documentation readiness, supplier alignment, and a disciplined approach to workplace conduct and communications. Even when the specifics differ by case, the risk pattern is often similar: disruption to normal operations, scrutiny over process integrity, and increased stakeholder attention.
In practical terms, a robust response plan focuses on three layers: (1) prevention and readiness—audits, training, and evidence collection; (2) rapid coordination—who decides, who documents, and how information flows; and (3) post-event remediation—corrective actions, supplier follow-through, and continuous improvement. The goal is not to “win” a narrative, but to demonstrate that the organization operates with lawful, consistent standards and can substantiate what it does.
For many organizations, the most expensive part of any intervention is not the event itself, but the downstream confusion: managers improvising answers, documents scattered across systems, inconsistent messaging, and unresolved control gaps. Those outcomes can compound quickly when multiple parties request information on overlapping timelines. The compliance priority, therefore, is to replace improvisation with a controlled and evidence-led system that can scale under pressure.
What “Unifor Raiding” Typically Signals in Workplace Contexts
Unifor Raiding is a term that appears in workplace discussions and sector reporting to describe targeted interventions connected to union activity, organizing, or verification of employment conditions. The word “raiding” is frequently used as shorthand; however, the underlying reality is usually administrative or investigatory scrutiny that can touch employment practices, contractor behavior, shop-floor procedures, and recordkeeping.
Because workplace interventions can involve multiple stakeholders—employees, management, contractors, unions, regulators, and sometimes third-party auditors—the compliance lens matters. Organizations that treat the issue as a purely operational challenge often experience avoidable friction. Those that treat it as a governance event—complete with controls, logs, and decision trails—tend to reduce uncertainty and improve outcomes.
In practice, organizations should assume that any workplace scrutiny can expose not just a single process gap, but the chain of accountability behind it. For example, if training completion records are incomplete, that may point to onboarding workflow issues, time reporting gaps, or a failure to refresh competency checklists. Similarly, if employee schedules are inconsistent with HR records, the root cause may not be “intentional wrongdoing,” but inadequate system controls or misalignment between operations and HR administration.
Accordingly, the compliance posture should be proactive and systems-driven. Rather than focusing only on what you think might be asked, focus on what you can evidence. Where evidence is missing, the system needs to be capable of rapidly reconstructing a defensible explanation (or correcting the underlying issue).
Early Warning Indicators and Why They Matter
Across industries that rely on shift work, subcontracting, and complex supply chains, organizations may see early indicators that something like Unifor Raiding could become a factor. While every situation is unique, common risk signals include:
- Increased employee concerns raised through formal channels or informal conversations that suggest process dissatisfaction.
- Contractor or supplier misalignment—especially where training, onboarding, or safety procedures differ from internal standards.
- Inconsistent documentation in HR, scheduling, attendance, or contractor compliance records.
- Sudden schedule pressure that leads to shortcuts in SOP adherence.
- External inquiries—letters, notices, or coordination requests—directed toward locations and responsible managers.
These indicators do not prove a specific outcome. They do, however, help management prioritize readiness. If a workplace intervention occurs, the ability to show consistent processes and complete records becomes a central asset. Without early readiness, the organization may still respond, but it often becomes reactive—collecting documents late, chasing sign-offs, and dealing with inconsistent manager narratives.
Another early-warning pattern involves control breakdowns that quietly accumulate. Examples include training modules delivered but not recorded, attendance recorded but not reconciled, policy updates issued but not acknowledged, or contractor onboarding checklists used for a period and then replaced with an informal “verbal confirmation” practice. These gaps can appear minor until someone requests the underlying evidence.
Organizations can treat early-warning indicators as inputs to a continuous improvement cycle. When employee concerns trend upward, review complaint handling and communication consistency. When contractor misalignment appears, revisit supplier onboarding and enforcement mechanisms. When documentation inconsistency rises, strengthen system validation and improve record governance.
Operational Risk: The Disruption You Can Plan For
From a risk-management perspective, the operational harm associated with Unifor Raiding isn’t only the immediate activity. The larger cost often includes downstream impacts:
- Shift disruption and altered access to work areas or records.
- Manager overload due to multiple simultaneous questions and documentation requests.
- Employee sentiment volatility, which can affect retention and productivity.
- Contractor uncertainty when responsibilities are unclear across tiers.
- Reputational exposure if communications are reactive or inconsistent.
To reduce this burden, organizations typically benefit from appointing a single incident coordinator, establishing a document-control workflow, and pre-drafting factual templates for internal and external communications (without making admissions or assumptions).
Operational planning should also address the human dimension of disruption. Even where the organization is confident in its compliance record, the workplace can become tense. Employees may worry about retaliation or misunderstanding. Managers may feel pressured to respond quickly rather than carefully. Contractors may fear consequences if they are perceived as non-compliant.
Therefore, operational risk planning should include practical measures such as controlled access to records, a clear “one voice” approach to stakeholder communications, and a calm “process explanation” script for managers. A well-designed operational response prevents employees from encountering contradictory instructions and reduces rumor amplification.
It can also help to define logistical steps: Where will documents be reviewed? Who will escort visitors? Which systems can be accessed and under what conditions? How will sensitive records be protected? Where possible, the organization should ensure that staff know the difference between answering a question and providing documentation. Many compliance issues arise when someone answers from memory without verifying details.
Compliance and Governance: What “Good Evidence” Looks Like
When an event related to Unifor Raiding arises, the organization’s credibility depends heavily on evidence quality. “Good evidence” usually means:
- Traceability: documents can be tied to dates, locations, and responsible roles.
- Completeness: policies, training logs, and recordkeeping aren’t partially missing.
- Consistency: what supervisors instruct aligns with what HR systems record.
- Controlled access: records are maintained under a defensible document governance process.
Even without knowing the specifics of a given case, these elements help an organization respond in a manner that is orderly, calm, and grounded in verifiable information.
Evidence readiness is not only about collecting documents; it’s also about how evidence is packaged. In many workplace interventions, multiple stakeholders request the same category of documents (for example, onboarding policies, training completion, or scheduling rules). If the organization does not have a repeatable evidence packaging workflow, it may spend significant time preparing documents repeatedly, increasing the chance of inconsistencies.
To strengthen governance, organizations often establish an evidence index or evidence binder structure. For example:
- Policy set with version history, effective dates, and acknowledgment mechanisms.
- Training set containing attendance lists, completion status, and module versions used.
- Work rules set that aligns with shift scheduling, attendance expectations, and escalation protocols.
- Contractor set reflecting onboarding, safety/behavior training, and reporting pathways.
- Incident and complaint handling set that shows how employee concerns are received, investigated, and resolved.
Additionally, governance should address document defensibility. If documents are altered after an inquiry begins, it can create credibility issues. Instead, evidence should be pulled as-of the relevant time period, and any corrections should be clearly documented as corrections (or documented improvements) that reflect an ongoing remediation commitment—not retroactive narrative shaping.
Industry Expert View: Supplier and Contractor Readiness
In many work environments, the practical reality is that organizations don’t control every variable. Contractors and suppliers manage day-to-day aspects of onboarding, training cadence, and sometimes certain workplace practices. For that reason, Unifor Raiding risk often becomes a multi-party governance problem.
Industry top practice is to treat suppliers as part of the compliance ecosystem. That generally includes:
- Confirming that supplier onboarding aligns with internal standards.
- Verifying that safety and conduct training is documented and periodically refreshed.
- Ensuring contractors understand reporting pathways for employee concerns.
- Clarifying what materials are provided, where records live, and who maintains them.
This approach reduces confusion if stakeholders request access to relevant materials or if management needs to demonstrate that employment and workplace standards are consistently applied.
Supplier readiness should be managed using both contract structure and operational controls. Contract clauses help define responsibilities and allow evidence-sharing pathways. Operational controls include ensuring onboarding checklists are enforced, training refresh schedules are tracked, and contractor managers are trained on what to do if questions arise.
In many organizations, contractor compliance fails not because contractors are unwilling, but because responsibilities are unclear. For example:
- Operations may believe HR is responsible for training records, while HR believes contractors hold those records.
- Supplier onboarding may be performed once, but the refresh schedule is not communicated.
- Conduct training may occur verbally, but no acknowledgment is collected.
- Reporting pathways may exist in policy, but contractor supervisors may not know how employees should raise concerns.
To address these patterns, organizations can require suppliers to provide periodic evidence packages (for example, quarterly training completion summaries) and require a clearly defined contact for compliance requests. This reduces scramble time and helps align expectations across tiers.
Another important aspect is ensuring that contractor behavior is within the same compliance culture as internal management. Workplace interventions often examine patterns: how supervisors speak, how policies are enforced, and whether employees feel safe raising concerns. If contractor supervisors provide inconsistent messaging, employees may interpret it as company endorsement or indifference. Therefore, contractor readiness should include messaging guidelines and escalation steps.
Communications Strategy: Be Factual, Not Performative
When Unifor Raiding is discussed publicly, narratives can spread faster than facts. An expert communications strategy typically follows these rules:
- Use neutral language focused on process integrity and readiness.
- Avoid speculating about motives or outcomes.
- Centralize approvals for any external statements.
- Maintain internal clarity to prevent rumors and conflicting instructions.
In day-to-day terms, employees benefit when leadership explains what is happening, what the organization can and cannot do, and where questions should be directed. That reduces uncertainty—a key driver of tension during workplace interventions.
Communications planning should also address “micro-communications.” For example, a manager might casually respond in an informal conversation with a detail they assume is harmless. In workplace scrutiny contexts, even casual comments can be quoted or summarized. Therefore, internal communications should define permissible topics and provide a short script that encourages staff to direct questions to the incident coordinator.
To support this, organizations often develop:
- Internal FAQs that answer common questions without speculation.
- Manager speaking guides for how to respond to employee questions calmly.
- External inquiry templates that can be customized only after legal/HR approval.
- Notification checklists so relevant stakeholders are informed at the right time (and not too early or too late).
Additionally, organizations should plan for the possibility that stakeholders use different channels. Employees may ask in person or via messaging; unions may send letters; regulators may contact responsible managers. The communications strategy should define a process for capturing all inquiries, routing them appropriately, and documenting responses.
Documentation is crucial in communications. If you say something, you should be able to show the basis for it. If you cannot evidence a claim, avoid making it. The goal is not silence, but careful clarity.
Price and Sourcing Considerations (What to Watch Without Overclaiming)
You may also see market chatter about “pricing” and “supplier costs” around compliance support, legal representation, or workplace services related to scenarios labeled as Unifor Raiding. Because pricing varies widely by jurisdiction, scope, and the depth of record review required, it is rarely appropriate to publish a single universal number.
From an objective procurement standpoint, what you can do is structure procurement decisions around measurable deliverables, such as:
- Document review hours and evidence packaging scope.
- Training session coverage and documentation templates provided.
- Incident coordination and policy-update turnaround times.
- Supplier audit readiness support and remediation planning.
If your organization is considering external support, the very defensible approach is to request proposals that itemize costs by deliverable, including assumptions and excluded services. That reduces surprises and helps compare supplier capability on a like-for-like basis.
Procurement due diligence should also evaluate how external service providers manage evidence handling, confidentiality, and communications. For example, a vendor may be strong in legal writing but weak in operational evidence indexing. Another vendor may be strong in training design but might not provide a documented methodology for audit trails. You can reduce procurement risk by requiring deliverables that produce usable outcomes for your internal governance system.
When comparing proposals, some organizations also evaluate:
- Methodology: how the vendor collects, reviews, and validates evidence.
- Quality controls: how errors are prevented in document packages and claims.
- Timeline transparency: how quickly documents can be assembled and reviewed.
- Escalation approach: who leads decisions if new evidence issues are discovered.
- Confidentiality and access controls: how sensitive records are protected.
In this way, “pricing” becomes less of a single number and more of a measure of how well you can achieve compliance readiness outcomes with minimal risk and disruption.
Localization Notes (“nearby” Use) and Practical Workplace Readiness
Your request included a localization constraint: anytime a city or country appears in keywords, replace it with "nearby." Since no city/country was explicitly provided in the supplied keywords, this guide keeps location references general. In practice, teams can tailor readiness checklists to the realities of their workplace—such as facility layout, access control points, and how records are stored for nearby operations or regional offices.
Even when a particular jurisdiction isn’t named, readiness planning still benefits from local operational mapping. This includes understanding:
- Who controls building access and how visitors are escorted.
- Where onsite personnel store paper records (if any) and how quickly they can be retrieved.
- Which systems are accessible within the facility (and which require secure remote access).
- How shift times affect evidence retrieval and document compilation timing.
- Whether there are different training versions used by different regions or contractors.
By tailoring the evidence packaging and operational response to the nearby facilities reality, organizations reduce the chance that a global policy exists but a local workflow breaks it.
Comparison Table: Actions, Source Type, and When to Use
Below is a supplement presented as a comparison table. It is intended to help organizations choose practical actions during periods when Unifor Raiding is part of the risk conversation.
| Action/Control | What It Aims to Validate | Source Type (Internal/External) | When to Apply | Typical Requirement/Condition |
|---|---|---|---|---|
| Policy and training evidence review | That procedures are documented and staff were trained | Internal HR & L&D records | Pre-event and immediately upon notice | Training logs must be date-stamped and role-mapped |
| Supplier compliance alignment audit | That contractors meet the same baseline standards | Internal compliance & supplier documentation | Pre-event and during supplier onboarding cycles | Access to contractor SOPs and onboarding checklists |
| Incident coordination protocol | Who leads decisions, approvals, and document control | Internal governance documentation | Activation when an intervention is anticipated | Named coordinator and backup roles must be current |
| Factual communications templates | Consistency and clarity without admissions | Internal communications policy | Before external inquiries and during event windows | Legal/HR review process for all statements |
| Post-event remediation plan | That gaps discovered are corrected and tracked | Internal corrective action records | After the intervention concludes | Corrective action owners and due dates assigned |
Step-by-Step Guide: Building Readiness Around Unifor Raiding
Because uncertainty increases costs, the very effective approach is a structured, repeatable readiness process. The steps below are designed to help organizations prepare for scenarios often described as Unifor Raiding, while keeping actions grounded in compliance and evidence practices.
-
Define scope and stakeholders.
Identify the impacted locations (including any nearby facilities you manage), business units, contractors, and internal owners. Establish a single incident coordinator and a backup.
-
Perform a “records readiness” check.
Audit core documentation: HR records, training logs, policies, onboarding materials, attendance and scheduling rules, and contractor compliance evidence. Ensure records are retrievable within a defined timeframe.
In this step, it helps to set a “maximum retrieval time” target (for example, within a day for standard requests). Even if you exceed it under exceptional circumstances, having a target improves operational planning and makes readiness measurable.
-
Verify supplier alignment.
Ask suppliers to confirm that their onboarding and safety/conduct expectations match your baseline requirements. Collect evidence such as training completion records and SOP acknowledgments.
Additionally, test whether supplier evidence can be shared quickly in a standardized format. If supplier records require manual conversion, build that into your readiness timeline.
-
Train managers on factual response boundaries.
Provide guidance on what can be explained, what must be documented, and how to avoid speculation. Emphasize calm tone and consistent messaging.
Training should include scenarios. For instance: “If asked whether an employee has been disciplined, what is permissible?” or “If asked why a schedule changed, how do you respond without guessing?” These scenario-based trainings reduce improvisation risk.
-
Set up a document-control workflow.
Use a controlled folder structure, versioning rules, and a log of what was shared and when. This is especially important during events where multiple parties may request information.
Make sure the workflow includes “document release tracking,” meaning a list of documents provided to whom and on what date. Without this, the organization may not be able to confirm what was shared, which can create additional compliance and credibility problems.
-
Run a tabletop exercise.
Simulate an inquiry and document requests. Test response times, escalation paths, and the completeness of your evidence packet.
Tabletops should include “messaging stress” and “evidence stress.” In other words: simulate the period where managers want to explain from memory and push back when evidence isn’t ready, then observe whether the incident coordinator can keep the response controlled.
-
Prepare a remediation backlog.
Define how you will capture gaps, assign owners, and measure completion after the event. This reduces the risk of “discussion without action.”
Make remediation backlog entries actionable: include root cause notes, corrective action steps, due dates, and verification method (for example, training completion confirmation, record system audit, or policy acknowledgment collection).
-
Review and iterate continuously.
After a tabletop exercise or any actual intervention, incorporate lessons learned into updated training, supplier terms, and audit frequency.
Continuous improvement should also cover staff turnover. If incident coordinator roles change, ensure the workflow and templates are updated and managers receive refresher training.
Conditions and Requirements: What Organizations Commonly Need Ready
While specific legal requirements vary by jurisdiction and the exact nature of the intervention, organizations generally benefit from meeting consistent internal conditions before any involvement described as Unifor Raiding occurs.
- Current role assignments for HR, compliance, operations, legal liaison, and communications approvals.
- Document accessibility for the records likely to be requested (training, onboarding, policy acknowledgments, and supplier evidence).
- Defined escalation criteria for when management should pause operational actions and shift to coordinated response mode.
- Supplier contract clauses that support compliance evidence sharing and remediation expectations.
- Consistent internal training so supervisors do not provide conflicting explanations to employees.
In addition to these conditions, organizations may find it useful to ensure their internal systems support audit-friendly retrieval. For example, HR systems can support queries by date range, location, and job role. Attendance and scheduling systems can show change history or approval logs. Training platforms can export evidence showing module name, version, completion date, and user mapping.
If these systems are not configured for quick export, the organization may need to do manual extraction during an event. Manual extraction introduces errors and inconsistencies, which can become part of the compliance scrutiny. Therefore, strengthening system retrieval capability is a major readiness lever.
Similarly, evidence storage policies should consider cybersecurity and confidentiality. A document-control workflow is not only about versioning—it’s also about restricting access to authorized persons and tracking access attempts. During an intervention, you may need to share evidence with external parties under certain restrictions. Controlled access reduces the chance of oversharing or misdirecting sensitive information.
FAQ: Unifor Raiding Risk, Compliance, and Response
1) What does “Unifor Raiding” mean in practice?
In practical workplace contexts, Unifor Raiding is commonly used as shorthand for targeted union-related interventions or scrutiny. The exact activities vary by case, but organizations should treat the event as a governance and compliance readiness scenario rather than an operational inconvenience alone.
Organizations often gain value by focusing on process rather than the label. Regardless of what the event is called externally, internally you should still manage it with the same core principles: evidence readiness, role clarity, and controlled communications.
2) Does preparation mean the organization is “at fault”?
No. Preparation is about evidence readiness and consistent processes. Well-prepared organizations can respond calmly and factually regardless of outcome, which reduces disruption and improves stakeholder confidence.
Preparation can actually strengthen trust among employees and contractors. When employees see that leadership has a clear process—an organized approach, consistent messaging, and evidence-handling standards—they may feel less anxious because the organization appears stable and accountable.
3) What documents are very important to have ready?
Typically, organizations should focus on policies and procedures, training and onboarding records, evidence of consistent supervisory practices, and supplier/contractor documentation that confirms aligned expectations. The specific list depends on your operational model.
It’s also useful to think in terms of “document categories” rather than single documents. Examples of document categories that often matter include:
- Workplace conduct and reporting policies (including how concerns are raised and how they are investigated).
- Training policies (with evidence of completion and refresh cycles).
- Scheduling and attendance rules (with records and change logs, where available).
- Onboarding checklists (especially contractor and supervisor onboarding materials).
- Records governance policies (how documents are retained, accessed, and updated).
This category approach helps ensure you don’t miss evidence even if the question asked changes slightly during the intervention.
4) How should communications be handled during a potential intervention?
Use a centralized approval approach and stick to verifiable facts. Avoid speculation about motives or outcomes. Provide employees with clear directions for where to ask questions, and ensure managers use consistent language.
For best results, communications should have three layers: internal employee messaging, manager guidance, and external inquiry responses. Each layer should be consistent in tone and content. The manager layer is especially important because managers tend to interact most frequently with employees and can unintentionally create inconsistencies.
5) How do suppliers affect Unifor Raiding-related risk?
Suppliers can introduce variability if their onboarding, training, or workplace standards differ from internal baselines. Supplier alignment—supported by documented evidence—is an important part of readiness because multiple stakeholders may request proof of consistent processes.
Supplier risk also includes the risk of information mismatch. For example, a supplier might believe their contractor supervisors were trained, but their records are incomplete or not easily retrieved. Or a supplier might follow a different escalation pathway. When stakeholder inquiries arrive, these mismatches become visible.
Therefore, supplier alignment should be both standards alignment (what should happen) and evidence alignment (how you can prove it happened).
6) Are there standard pricing ranges for compliance support?
Pricing is highly variable and depends on scope, the number of locations involved, and the depth of document review required. A defensible approach is to compare vendors based on deliverables, assumptions, timelines, and evidence handling processes rather than relying on generic price ranges.
Even if you see market rates, the more important question is whether the vendor’s process produces audit-ready documentation quickly and reliably. A slightly higher cost may be less risky if it results in higher evidence quality, fewer revisions, and clearer escalation handling.
7) What should we do immediately if we receive notice?
Activate your incident coordinator, secure and log relevant documents, confirm roles for stakeholder communication, and begin a records-readiness check. Then coordinate with HR/compliance/legal as appropriate to ensure the response stays factual and consistent.
Immediate steps can also include implementing a “pause and validate” rule for managers. This means that if someone wants to provide an answer that depends on internal records, they should pause and route to the incident coordinator or evidence owner until the documentation is verified.
Additionally, organizations should ensure that document access and handling is logged. If multiple parties access systems, it becomes harder to manage confidentiality and to defend what was accessed, when, and why.
8) What does a strong post-event remediation plan include?
It should track discovered gaps to closure with responsible owners and due dates. The plan should update training, procedures, and supplier expectations where improvements are needed, and it should be reviewed for continuous improvement.
A remediation plan should not only list issues; it should include root cause analysis. For example, missing training evidence might be caused by:
- Training delivered but not recorded due to system integration problems.
- Manual attendance entries not reviewed for completeness.
- Supervisor onboarding not being mapped to HR systems correctly.
- Supplier onboarding evidence not being collected in a standardized format.
When root cause is identified, corrective actions are more targeted and verification becomes more realistic.
Reliable Context: Evidence-Based Governance Without Overclaiming
Your request emphasizes avoiding unverified or exaggerated data. In that spirit, this guide refrains from publishing quantitative claims about the frequency or outcomes of events labeled Unifor Raiding. Instead, it focuses on general, evidence-based governance practices that apply across workplace and compliance settings. For legal or regulatory interpretation specific to your jurisdiction, consult qualified counsel and refer to applicable official guidance from relevant labor and workplace authorities.
It’s also important to avoid overclaiming what readiness “guarantees.” Evidence readiness reduces risk and improves response clarity, but no organization can guarantee an outcome. Stakeholder perspectives vary, and workplace interventions can uncover issues that were previously unknown. The governance goal is not to guarantee perfection; the goal is to ensure that if scrutiny happens, the organization can explain and substantiate its practices and correct gaps responsibly.
In that sense, the readiness program should be designed as a resilience system. Resilience means: the organization can keep operations running as much as possible, can respond without chaos, can preserve credibility, and can learn and improve after the event.
Closing Perspective: Make Readiness a System, Not a Reaction
Whether the term Unifor Raiding is used in media coverage, internal risk discussions, or supplier briefings, the organizational lesson is consistent: successful handling depends on disciplined readiness. Build documentation control, align suppliers, centralize communications, and run tabletop tests. When the unexpected arrives, your organization should be able to respond with clarity—showing that operations are governed, records are maintained, and stakeholders are treated with professionalism.
A system-based approach also helps reduce internal stress. When managers know there is an incident coordinator, a document-control workflow, and an approved communications process, they feel less compelled to “wing it.” Employees benefit from consistent messaging and predictable processes. Contractors and suppliers benefit from clear evidence-sharing expectations.
In the long run, readiness investments often pay back through improved audit readiness, clearer training systems, and stronger supplier onboarding. Even when a labeled event never occurs, the organization still benefits from better governance and clearer accountability structures.
Cover Note (Image Use)
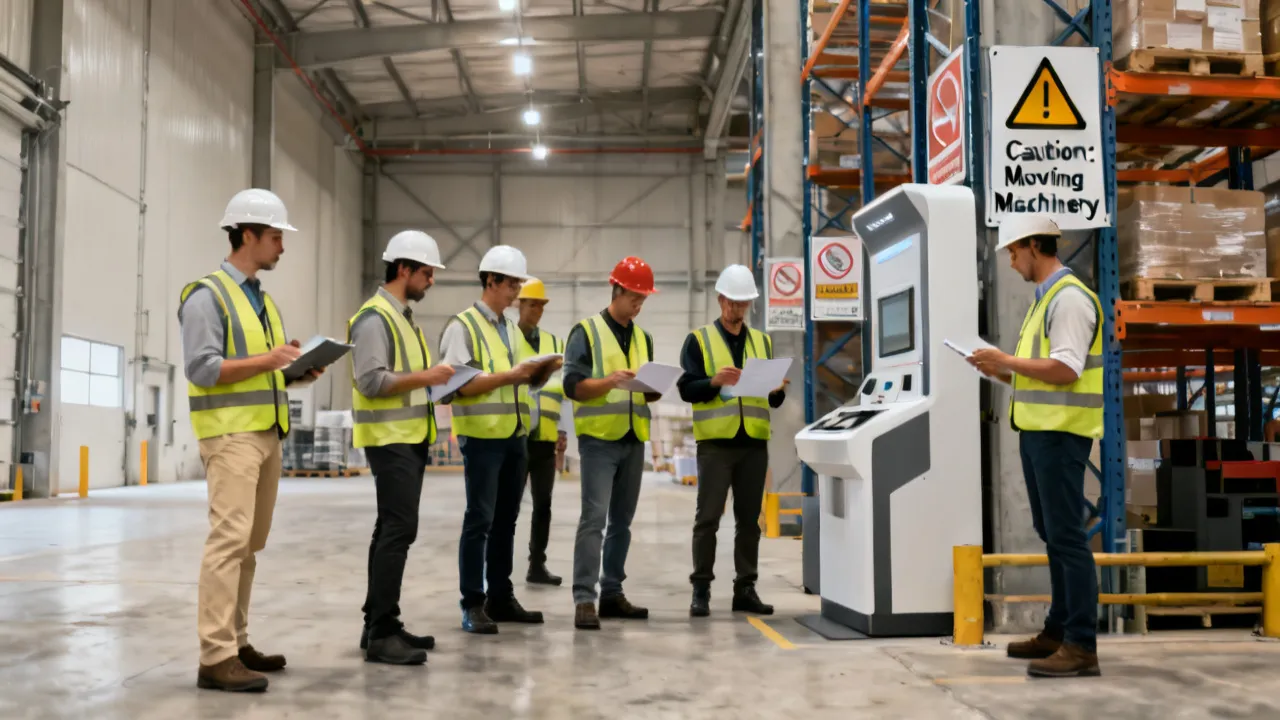
The cover image prompt provided at the top is designed to reflect a calm, compliant inspection atmosphere—appropriate for illustrating workplace readiness and governance rather than sensationalism.